
Overview
Trendemon’s AI assistant, SAIL, allows authenticated Trendemon users to ask natural-language questions about their website traffic, engagement, conversions, campaigns, content, audiences, and personalization performance.
Trendemon sends the user’s question to the OpenAI API. When account data is required, OpenAI calls Trendemon’s MCP server, which retrieves approved, account-scoped analytical data through a controlled query layer. The generated answer is then returned to the Trendemon dashboard.
This differs from a customer-managed MCP integration: SAIL uses Trendemon’s internal MCP server as part of the application flow. Customers do not configure a separate MCP client or authenticate directly with OpenAI.
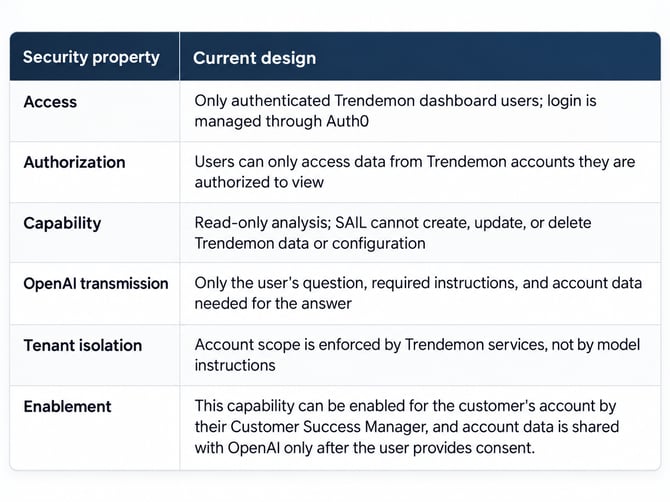
Architecture and data flow
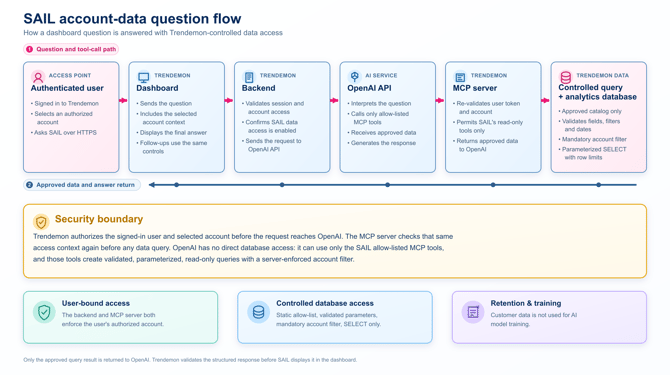
When a user submits a question:
1. User → Trendemon dashboard
The authenticated user submits a question to SAIL over HTTPS. The user’s Trendemon account is already associated with their authenticated session.
2. Trendemon dashboard → Trendemon backend
The dashboard sends the question and the user’s account context to the Trendemon backend using the authenticated session.
3. Trendemon authentication and authorization
Trendemon validates the user’s session, confirms that the user may access the associated account, and verifies that SAIL account-data access is enabled.
4. Trendemon backend → OpenAI API
The backend sends the question and instructions to the OpenAI API, together with access to a restricted set of Trendemon MCP tools. OpenAI does not receive direct database access.
5. OpenAI API → Trendemon MCP server
When account data is required, OpenAI calls an approved read-only MCP tool. The MCP server re-validates the user and associated account before processing the request.
6. Trendemon MCP server → Controlled analytics database
The MCP server validates the requested table, fields, filters, and date range against an approved analytics catalog. It then creates a parameterized read-only query with a mandatory server-enforced account filter.
7. Controlled data → OpenAI API
Only the approved, account-scoped query result is returned through the MCP server to OpenAI. OpenAI uses this data to generate the answer.
8. OpenAI API → Trendemon backend → User
The generated response returns to the Trendemon backend, where its structure is validated before it is displayed in the authenticated SAIL dashboard. Follow-up questions remain subject to the same authorization and data-access controls.
Authentication, authorization, and query safety
SAIL uses the existing Trendemon identity and permission model. The user does not need an OpenAI account, and OpenAI credentials remain server-side.
Only users who can authenticate to the Trendemon platform and access the relevant account can ask SAIL questions about that account's data.
Controlled analytics access
- Only approved tables, dimensions, metrics, and filterable fields are available.
- The assistant uses structured query parameters rather than arbitrary SQL.
- Filter values are bound as parameters, and the validated account ID is added server-side as a mandatory filter.
- Date ranges, result rows, payload size, execution time, model tokens, and request frequency are limited.
- Generated output is treated as untrusted text, safely encoded for display, and never executed as HTML, JavaScript, SQL, or a privileged Trendemon action.
Data sent to and processed by OpenAI
SAIL uses aggregated Trendemon analytics data in the following domains:
- Traffic and traffic sources
- Conversions
- Audiences
- Content performance
- Campaign performance
- Trendemon personalization-unit performance
- Coverage and uplift data
Trendemon sends the user’s question to OpenAI. When analytical data is required, OpenAI receives only the approved, account-scoped query results returned through Trendemon’s MCP server.
Trendemon does not send visitor-level data to OpenAI.
Trendemon also does not send:
- Personally identifiable information (PII)
- Direct CRM data
- Direct Marketing Automation data
- OpenAI credentials
- Authentication tokens, credentials, and secrets are not included in prompts or analytical data returned to the model. Authentication information is used only to authorize the controlled MCP connection.
The data available to SAIL is limited to the approved analytical dataset exposed through Trendemon's controlled data layer.
For additional details about the supported data types and examples of questions that can be asked, see this use cases article.
AI training
Customer data, including data submitted as part of a SAIL question, is not used by Trendemon for AI model training.
Customer data submitted through SAIL is also not used to train or improve the underlying OpenAI model under Trendemon's OpenAI API usage.
This includes the data supplied with the request, user prompts, and generated responses.
Data retention
Trendemon does not currently use OpenAI’s Zero Data Retention control. SAIL operates under OpenAI’s standard API data controls. OpenAI may retain customer content, including prompts and responses, in abuse-monitoring logs for up to 30 days, subject to limited legal and safety exceptions.
SAIL uses stored Responses API state to support conversation continuity and follow-up questions. Under OpenAI’s standard configuration, this response data is stored for at least 30 days. The information processed may include the user’s question, approved account-scoped analytical data returned through Trendemon’s MCP server, and the generated answer.
OpenAI does not use data submitted through its API to train or improve its models unless the API customer explicitly opts in to data sharing. Trendemon separately retains SAIL activity records according to Trendemon’s own retention policies.
LLM provider, hosting, and data location
Trendemon customer data is hosted in AWS in the United States.
Trendemon currently uses OpenAI as the LLM provider for SAIL. The specific OpenAI model used may change over time as Trendemon evaluates quality, performance, availability, and security requirements.
When SAIL processes an account-data question, the relevant approved data is transferred from Trendemon's AWS environment to the OpenAI API over TLS for AI processing.
Customers do not connect directly to OpenAI, and OpenAI credentials remain managed by Trendemon server-side.
Database access and security controls
The LLM does not have unrestricted direct access to Trendemon's production database.
Instead, SAIL accesses data through a controlled, read-only analytical layer.
All AI-driven data access is read-only. The AI cannot execute write operations such as: INSERT, UPDATE, DELETE.
The model also cannot perform schema changes or privileged Trendemon actions.
The analytical catalog is a static, code-defined allow-list. The LLM can only request approved tables, fields, metrics, dimensions, and filters that Trendemon has explicitly made available.
Trendemon constructs and validates the query rather than allowing the LLM to execute arbitrary SQL.
Tenant isolation and prompt injection protection
SAIL uses the same authentication and account-access controls as the Trendemon dashboard.
When a user asks a question:
- Trendemon validates the user's authentication token.
- Trendemon determines which account the user is authorized to access.
- The validated account ID is applied server-side to the data request.
- Only data associated with that account can be returned.
The account filter is enforced by Trendemon's application and query layer and cannot be removed or changed through a user prompt.
This prevents a user from requesting another customer's data simply by asking SAIL to access it.
SAIL also limits the actions available to the AI through a controlled catalog of approved tables, columns, metrics, and filters. As a result, prompt injection cannot grant the LLM additional database privileges.
A malicious prompt cannot instruct the AI to:
- Remove the mandatory account filter
- Access another customer's account
- Retrieve unauthorized tables or fields
- Execute arbitrary SQL
- Run INSERT, UPDATE, or DELETE operations
- Retrieve credentials or secrets
- Perform privileged Trendemon actions
Generated output is also treated as untrusted text and is not executed as code or as a database command.
User permissions
SAIL follows the existing Trendemon authentication and account-access model.
The user's Auth0 session is validated in the same way as when accessing the Trendemon dashboard, and data is retrieved according to the account the user is authorized to access.
SAIL therefore does not provide an alternative route for accessing an account that the user cannot otherwise access through Trendemon.
Only authenticated Trendemon platform users with access to the relevant account can retrieve that account's data through SAIL.
Accuracy and hallucination controls
SAIL is designed to ground analytical and numerical responses in actual Trendemon data.
Several controls help reduce the risk of hallucinated metrics:
- The model receives actual Trendemon data retrieved in response to the user's question.
- Data can be retrieved only from the approved analytics catalog.
- The AI does not generate unrestricted SQL.
- Metrics, dimensions, filters, and account scope are constrained by Trendemon's controlled query layer.
- The validated account ID is applied server-side.
- Result sizes, date ranges, payload sizes, execution time, and token usage are limited.
- Follow-up questions remain subject to the same data-access controls.
These measures help ensure that numerical answers are grounded in the Trendemon dataset provided to the model rather than generated from general model knowledge.
As with any generative AI system, however, the LLM may still incorrectly interpret or summarize valid data. Users should validate business-critical findings against the relevant Trendemon dashboards and reports.
Trendemon also logs the question, response, and data accessed, which can be used for troubleshooting and further validation.
Audit logs
Trendemon keeps logs of SAIL activity, including:
- The questions submitted
- The responses generated
- The data accessed in connection with the request
These records can be used for troubleshooting, security review, and audit purposes.
If required, Trendemon can provide a report containing the relevant SAIL activity information.
Data shared with OpenAI
Read-only tools, including:
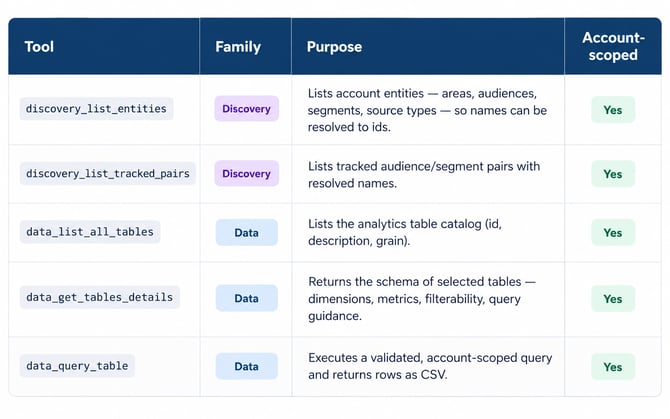
The list of tools is dynamic and Trendemon keeps adding relevant tools to conduct the data analysis required.
The analytics catalog is a static, code-defined allow-list of aggregated tables, at daily and monthly grain, covering traffic, conversions, coverage, sources, campaigns, unit performance, and uplift — including their ABM, or company-level, counterparts.
It is not a generic SQL gateway: the model cannot name a table, column, or expression that is not in the catalog.
All access through these tools is read-only and restricted to the validated Trendemon account.
Security and privacy summary
In summary:
- SAIL is available only to authenticated Trendemon users.
- Users can access data only for Trendemon accounts they are authorized to access.
- Account isolation is enforced server-side.
- Data access is read-only.
- The LLM does not have unrestricted direct access to Trendemon's production database.
- Only predefined analytical tables, metrics, dimensions, and filters are available.
- The AI cannot execute arbitrary SQL.
- The AI cannot perform INSERT, UPDATE, or DELETE operations.
- SAIL uses aggregated analytics data.
- Visitor-level data is not sent to the LLM.
- PII is not sent to the LLM.
- Direct CRM and marketing automation data is not sent to the LLM.
- Authentication tokens, credentials, and secrets are not included in prompts.
- Customer data is not used for AI model training.
- Model output is treated as untrusted text and cannot execute code, SQL, or privileged Trendemon actions.
- Questions, responses, and data accessed are logged for audit and troubleshooting purposes.